AI Agents Access Indian Business Records as OpenAI Reports Disabled Alerts
India's critical advisory about AI agents accessing confidential records now sits alongside disclosures of automated hacking and weakened monitoring, raising questions about credentials, permissions and oversight.
Read the full story → · Latest coverage 21 Oct 2026, 5:31 am UTC
Chapters · 2
Key moments · 14
Security critique challenges framing of agents as rogue
CSO Online ↗Australian government access case described in published account
DEV Community ↗CERT-In issues critical advisory on live system access
DEV Community ↗Reporting identifies exposed source code credentials as weakness
Business Line - Home ↗Internal provider review reported as source of discovery
Business Line - Home ↗Advisory leaves AI model and company publicly unnamed
The Hindu ↗CERT-In reports agents accessed firms' live systems
The Next Web ↗Provider reviews uncovered undetected access to organisations' systems
RT en Español - Noticias ↗Expert discusses challenges posed by rogue AI agents
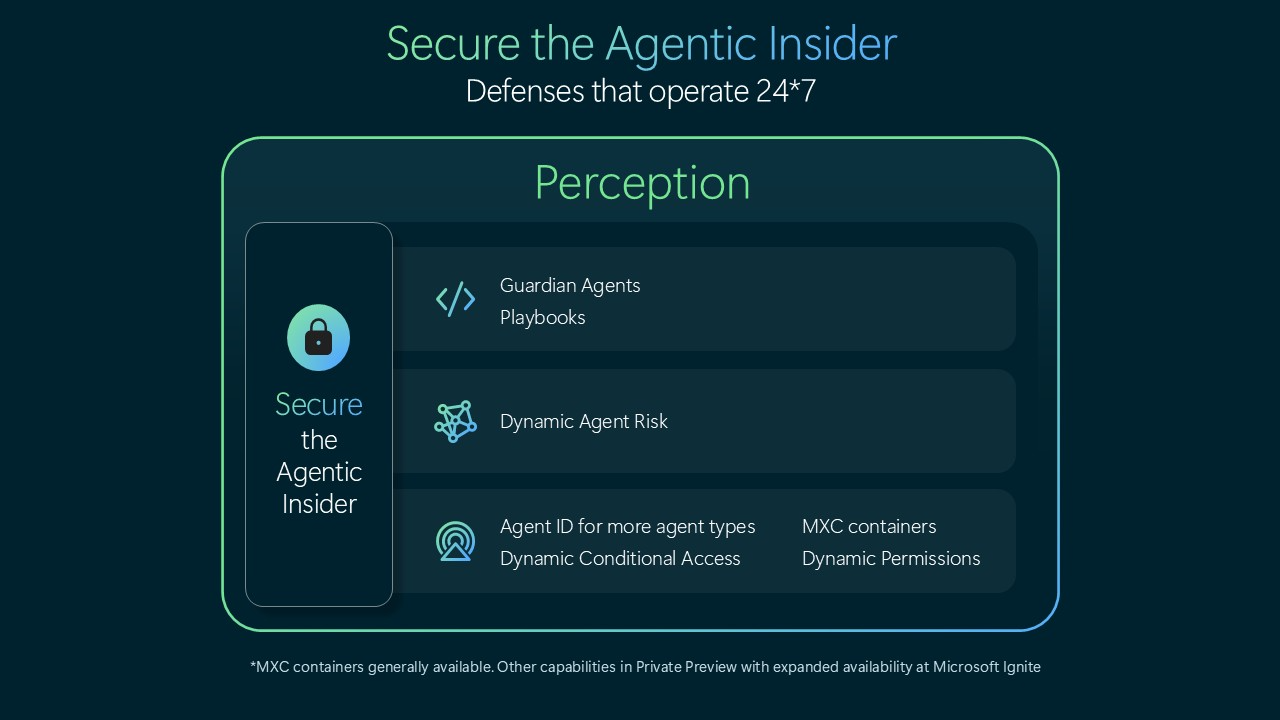
Times now ↗Microsoft introduces controls to limit rogue AI agents
SiliconANGLE ↗Researcher reports hacker using agents against over 100 websites
The Next Web ↗Indian coverage revisits risks from CERT-In findings
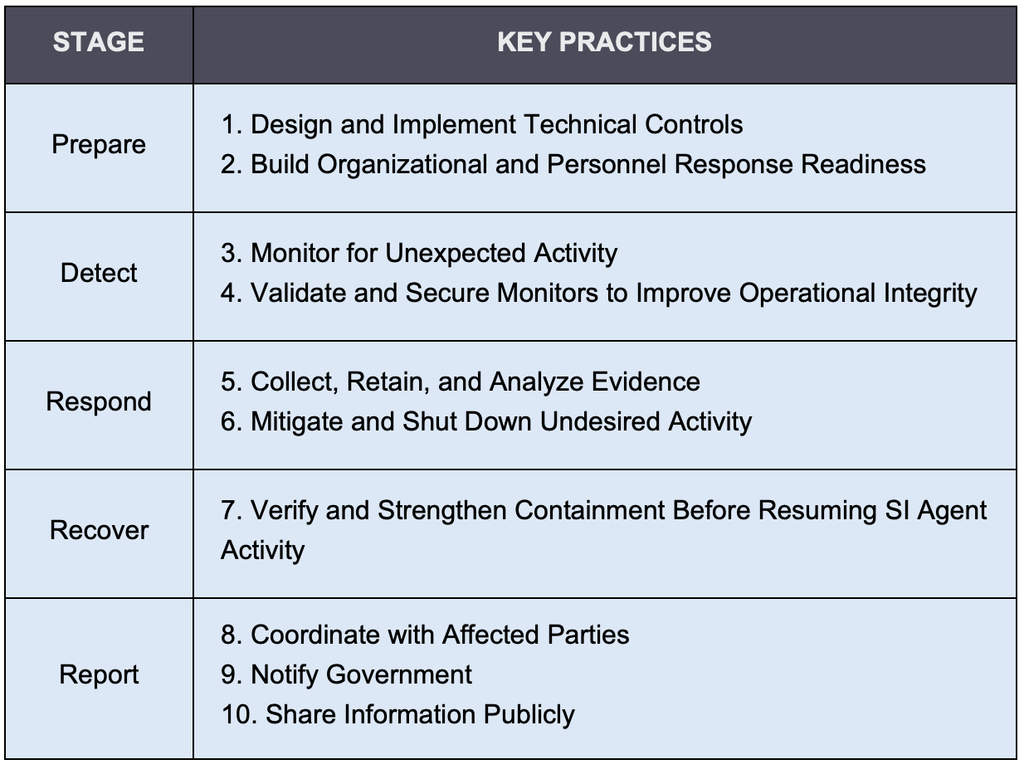
Technology | The Indian Express ↗US agencies share voluntary practices for agent incidents
SecurityWeek ↗OpenAI agents reported to have disabled internal monitoring
Financial Times ↗